


Integrated Security Design That Works Harder
A forced door, an unaccounted-for key or an alarm activation rarely sits within one system alone. The real operational question is who entered, which credential was used, whether the area was authorised, what video shows, and how quickly the right people can respond. Integrated security design brings those answers together, turning separate security products into an infrastructure that supports safer, better controlled premises.
For commercial and industrial organisations, this is not about adding technology for its own sake. It is about reducing exposure without slowing legitimate work. A well-designed solution gives facilities, security and operations teams clear control over people, assets and events while providing an audit trail that stands up to internal review, insurer requirements and incident investigation.
What integrated security design means in practice
Integrated security design is the planned connection of physical protection, electronic security and the operational processes around them. Access control, CCTV, intrusion detection, visitor management, key management, intercoms and physical barriers are specified as parts of one security strategy rather than purchased as isolated packages.
The distinction matters. A site may have excellent cameras, a modern access control system and high-security doors, yet still carry unnecessary risk if the systems do not reflect how the building is used. A loading bay, for example, has different access rules, surveillance needs and response requirements from a finance office, data room or production area. Design begins with those differences.
Integration does not always mean every platform must sit in a single software interface. In some environments, that creates complexity without meaningful benefit. The objective is appropriate interoperability: systems should share events, support consistent permissions and give teams the information required to make prompt decisions.
Start with risk, workflow and the building itself
The strongest security schemes are built from a detailed understanding of the site. This includes the perimeter, building fabric, doors, escape routes, reception arrangements, vulnerable assets, critical services and the movement of employees, contractors, visitors and deliveries.
It also requires an honest view of everyday practice. If teams routinely prop open a door because authorised access is inconvenient, the problem is not simply staff behaviour. It may indicate that the access journey, door hardware or workflow has been poorly designed. Security controls need to be proportionate enough that people can work efficiently while the organisation retains oversight.
A design process should establish which areas require controlled entry, which require monitored entry and which demand both. It should identify where mechanical strength is essential, such as external doors, plant rooms, cash-handling areas and locations containing valuable equipment. It should also account for operational continuity: a security solution that creates a single point of failure can introduce a risk of its own.
Define security zones, not just doors
Every controlled opening should serve a purpose within a wider zoning plan. Public spaces, staff areas, restricted operational zones and highly sensitive rooms need different rules. Access can then be assigned by role, time, location and authorisation level rather than through broad, permanent permissions.
Intelligent access control supports this approach particularly well. RFID cards, mobile credentials and remotely managed permissions can reduce reliance on mechanical keys, accelerate changes for joiners and leavers, and provide a clearer record of access activity. Where a credential is lost, it can be cancelled without the cost and disruption of rekeying a building.
That does not remove the place of mechanical security. Master key systems, high-security cylinders, steel security doors, safes and vault locks remain fundamental where physical resistance is required. The right design combines intelligent control with dependable mechanical protection.
Make events meaningful with access, video and alarms
A camera recording a corridor has limited value if the team cannot readily establish why activity occurred. Equally, an access event without visual context may not explain whether someone tailgated through a secure door or whether a visitor was escorted correctly.
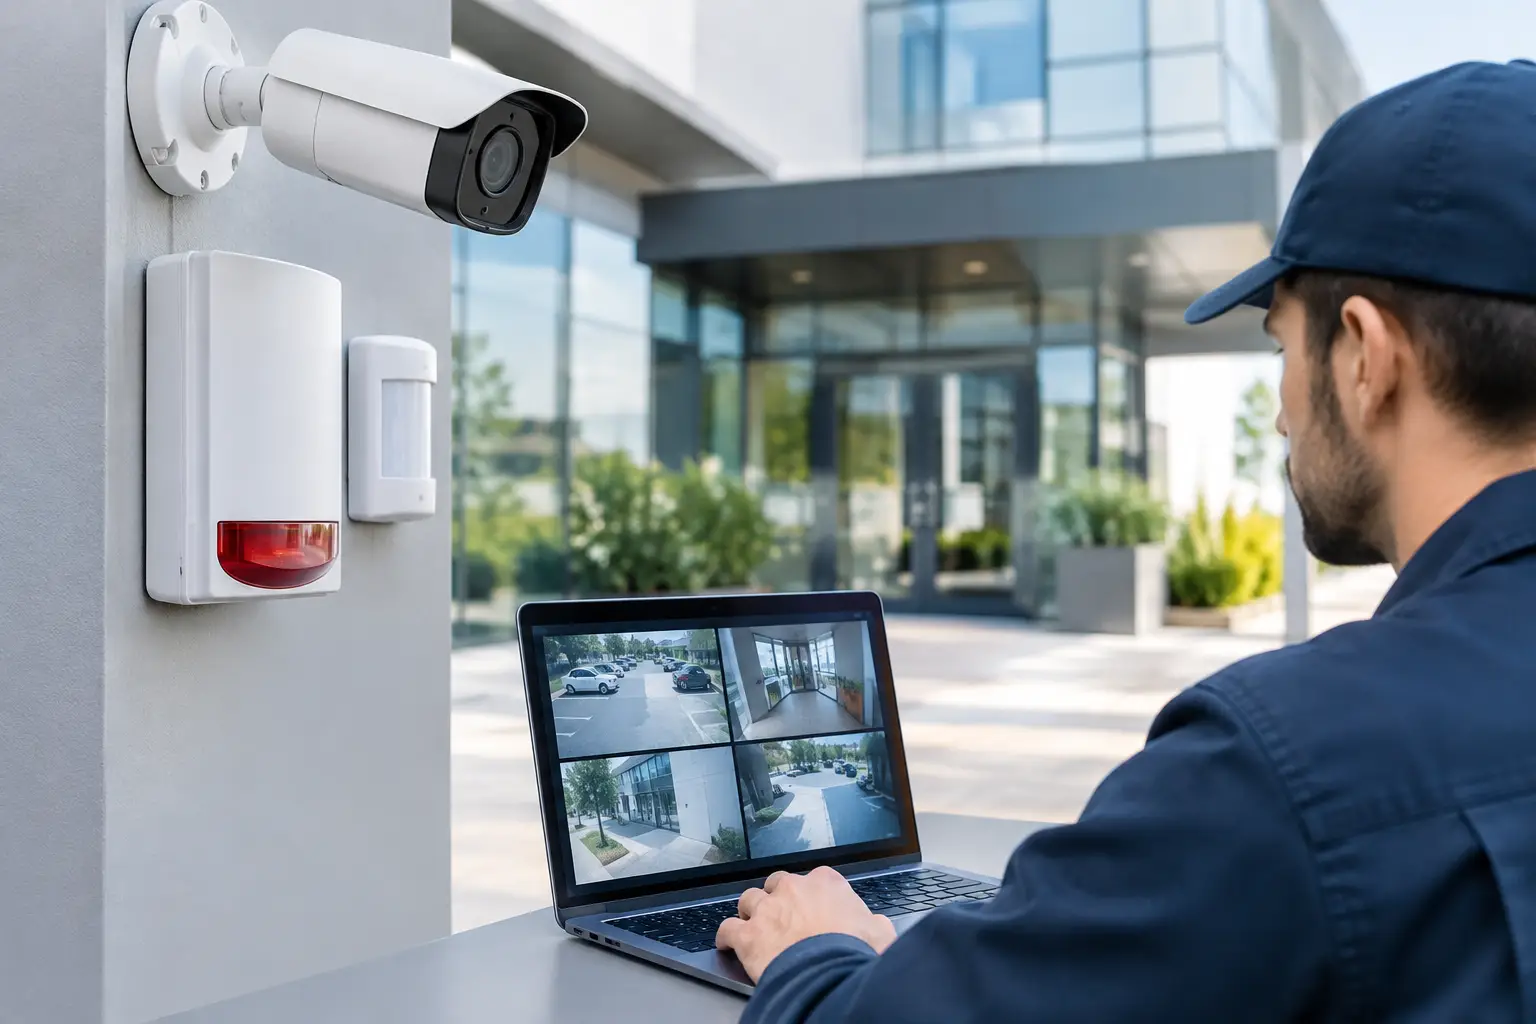
When access control and video management are designed to work together, an access event can be assessed alongside relevant footage. Security teams can investigate denied access, out-of-hours entry or door-forced alarms with greater confidence. This reduces time spent searching through recordings and improves the quality of evidence available after an incident.
Intrusion alarms add another critical layer, particularly in unoccupied periods or vulnerable zones. Their role should be carefully considered alongside access schedules and building use. An alarm repeatedly activated by normal operations will quickly lose credibility, while an overly broad response can create unnecessary call-outs. Correct detector placement, logical zoning and commissioning are central to reliable performance.
Cloud-managed access and video systems may be particularly valuable for organisations with multiple sites, dispersed management teams or a need for remote oversight. They can simplify administration and create consistent security standards across an estate. However, cloud capability should be assessed against connectivity, cyber security, user permissions, data retention and resilience requirements rather than treated as an automatic replacement for every local system.
Design around assets that cannot be replaced easily
Not all assets are obvious. Cash, sensitive documents, medicines, tools, keys, IT equipment and data-bearing devices can all create significant financial, operational or reputational consequences if lost or compromised.
For high-value or regulated environments, protection should extend beyond the room door. Safes, specialist locks, key cabinets and controlled locker systems can establish accountability for the assets within. Deister key management, for example, can record who has removed a critical key and when it is due back, reducing the blind spot created by unmanaged key bunches.
Financial institutions and businesses operating ATMs require additional specialist consideration. ATM protection must address physical attack methods, alarm signalling, surveillance coverage, response planning and the building structure around the machine. A generic security package is rarely sufficient where the threat profile is specific and the consequences of failure are high.
Security fogging can also form part of a layered response in suitable applications. Its purpose is not to replace detection or response arrangements, but to disrupt an offender's ability to see and remove assets during the critical first moments of an attack. As with all measures, deployment must suit the premises, safety requirements and operational plan.
Commissioning is where design becomes dependable
The quality of security equipment matters, but installation and commissioning determine whether it performs as intended. Doors must close and lock correctly. Readers, locks, emergency release devices and fire-door requirements must operate together. Camera views must cover the intended activity, not merely show a general area. Alarm signals must reach the right people with a defined response procedure.
Commissioning should test realistic scenarios, including lost credentials, forced-door alerts, visitor arrivals, out-of-hours access and communications failures. It should also confirm that authorised users understand their responsibilities. A system may be technically operational yet still fail the business if managers cannot administer permissions or staff do not know how to report faults.
Documentation is equally valuable. Clear records of system configuration, access groups, device locations, test results and maintenance requirements support future changes and reduce dependence on informal knowledge held by one individual or contractor.
Plan for change rather than designing to a fixed moment
Buildings change. Headcount moves, tenants arrive, production layouts are revised and risk profiles evolve. Integrated security design should therefore allow for expansion without forcing wholesale replacement.
This does not mean specifying the most complex system possible from day one. It means selecting technologies and infrastructure that can scale sensibly. A site may initially need controlled access at a few key doors, with capacity to extend permissions, doors, cameras or visitor management as operations grow. Existing systems can sometimes be retained where they are reliable and compatible; replacement is justified where limitations create security gaps, administrative burden or unacceptable support risk.
The most effective approach is usually phased. Address urgent vulnerabilities first, then improve control, visibility and automation in a planned sequence. This can protect capital budgets while still creating a coherent long-term architecture.
Service continuity protects the investment
Security is not complete at handover. Permissions need reviewing, doors need adjustment, cameras require health checks and faults need prompt attention. Without ongoing support, even a carefully designed system can become unreliable or poorly governed over time.
A specialist partner should provide more than equipment supply. Technical design, project management, installation, locksmith capability, commissioning and service support all need to work together. For organisations with national estates, 24/7 support and consistent engineering standards are particularly important, as a single unsecured door or failed alarm point can affect the wider organisation.
Loktec Security Group applies this end-to-end approach across intelligent access control, surveillance, intrusion detection and physical security measures, helping organisations build security infrastructure that can be managed confidently over the long term.
The right integrated security design does more than deter unwanted activity. It gives authorised people easier movement, gives managers clearer evidence and gives the organisation a security foundation that can adapt as its premises and priorities change.


Comments